SASE: 13 Powerful Benefits, Components & Implementation Guide
Description
Learn what SASE is, how its architecture works, its key components, use cases, benefits, challenges, and implementation steps for modern networks.
Scope
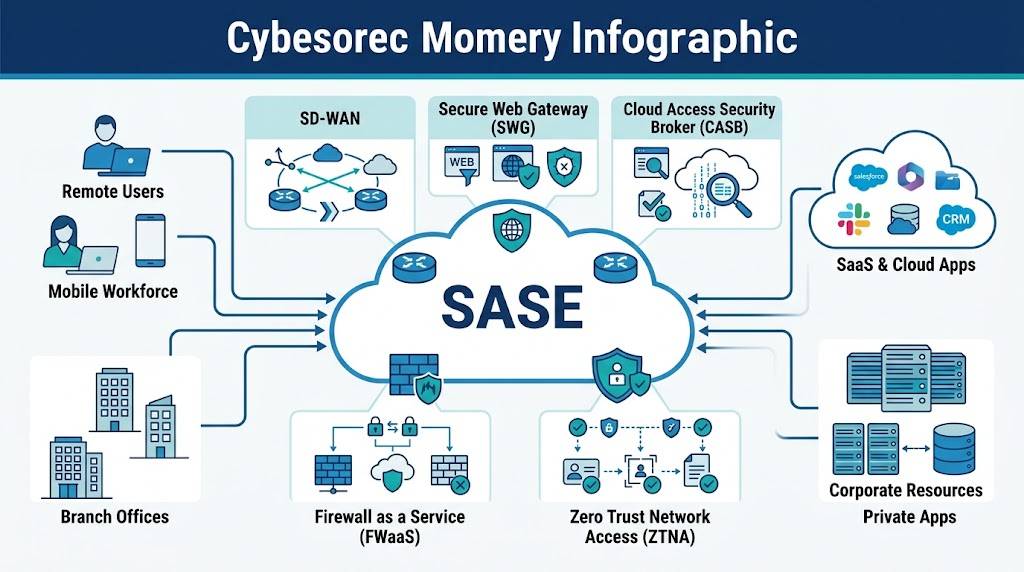
Secure Access Service Edge (SASE) is a cloud-native architecture designed to combine networking and security capabilities into a unified service. It brings together SD-WAN, Secure Web Gateway (SWG), Cloud Access Security Broker (CASB), Firewall as a Service (FWaaS), and Zero Trust Network Access (ZTNA).
This guide explains SASE architecture, its main components, use cases, benefits, implementation challenges, provider selection criteria, implementation steps, common myths, complementary technologies, and comparisons with other networking and security approaches.
1. What Is SASE?
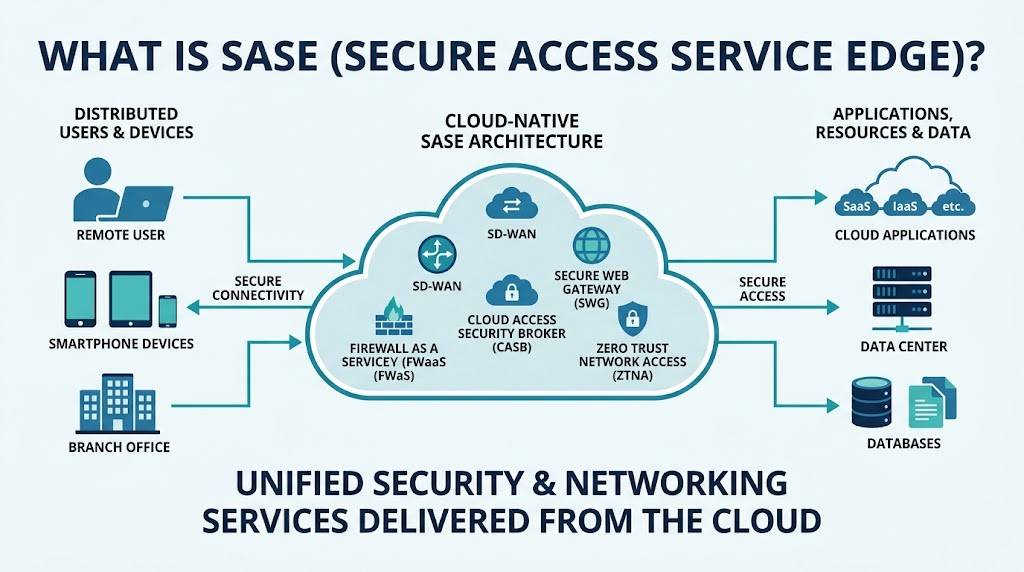
SASE, pronounced “sassy,” stands for Secure Access Service Edge. It is a cloud-native architecture that combines networking and security services into a unified approach.
SASE brings together:
- Software-Defined Wide Area Networking (SD-WAN)
- Secure Web Gateway (SWG)
- Cloud Access Security Broker (CASB)
- Firewall as a Service (FWaaS)
- Zero Trust Network Access (ZTNA)
By combining these capabilities, SASE provides secure connectivity and security controls for users, applications, devices, and data across modern distributed environments.
2. Why Do Businesses Today Need SASE?
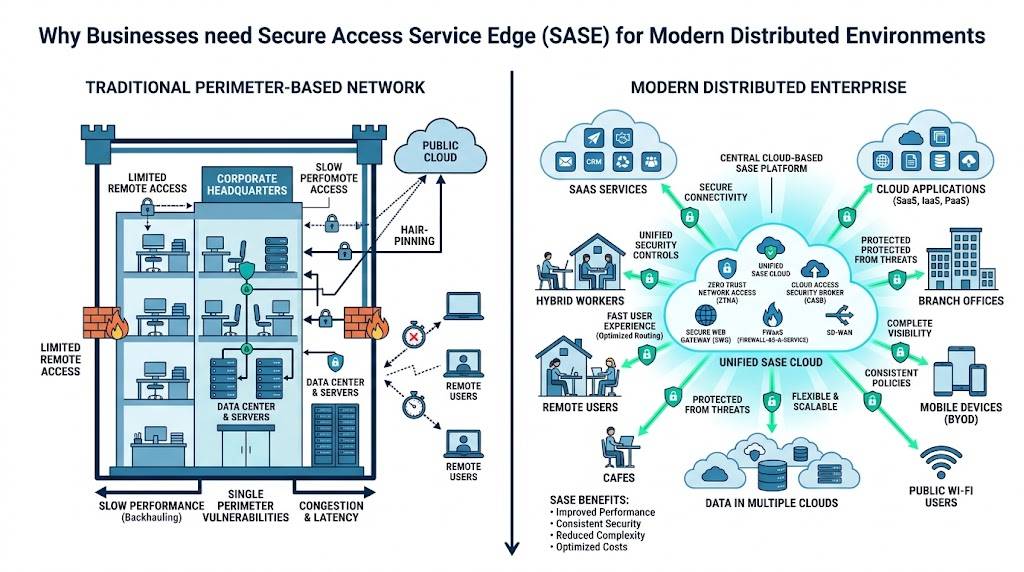
Cloud adoption, mobile users, and remote and hybrid work have changed how organizations access applications and data, increasing the need for solutions such as SASE. Users and resources are no longer located only inside a traditional corporate network.
As a result, traditional perimeter-based security approaches can become less effective for distributed environments, increasing the need for SASE.
The source references the Rackspace 2025 State of Cloud Report, which reports that 92% of workloads are in the cloud.
It also references Gartner research from 2023, which projected a 29% compound annual growth rate for the SASE market and a market value above $25 billion by 2027.
These changes help explain why organizations are looking toward cloud-based networking and security architectures such as SASE.
3. What Is SASE Architecture?
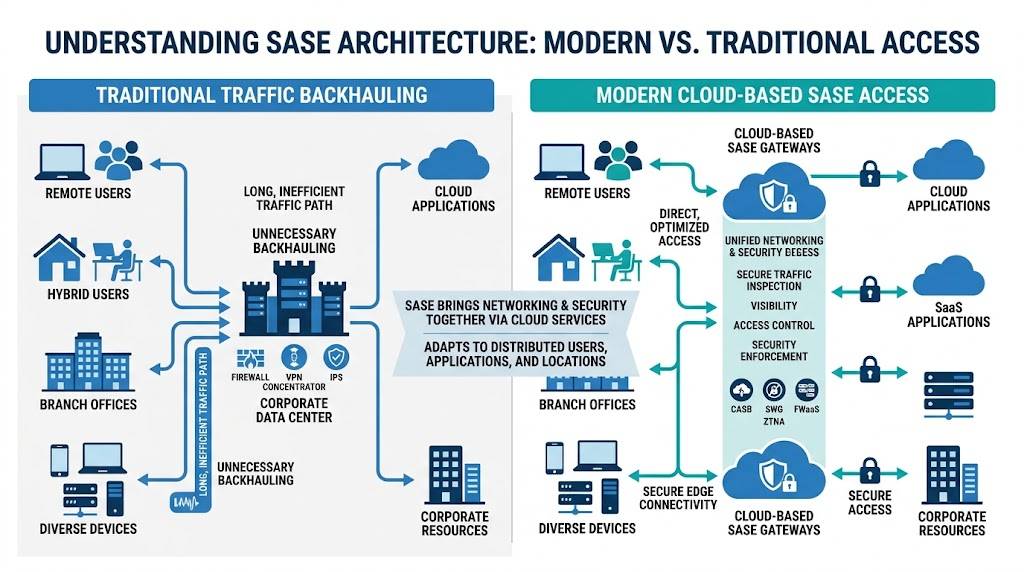
SASE architecture brings networking and security capabilities together through cloud-based services.
Instead of requiring remote and hybrid users to send traffic back through centralized corporate data centers, SASE allows users to connect to nearby cloud gateways. This approach can provide consistent and secure access to applications while reducing unnecessary backhauling.
The architecture can provide visibility and inspection across network traffic, including different ports and protocols. It can also simplify management by bringing networking and security capabilities into a more unified architecture.
The cloud-based approach allows the network and security environment to adapt to distributed users, applications, and locations.
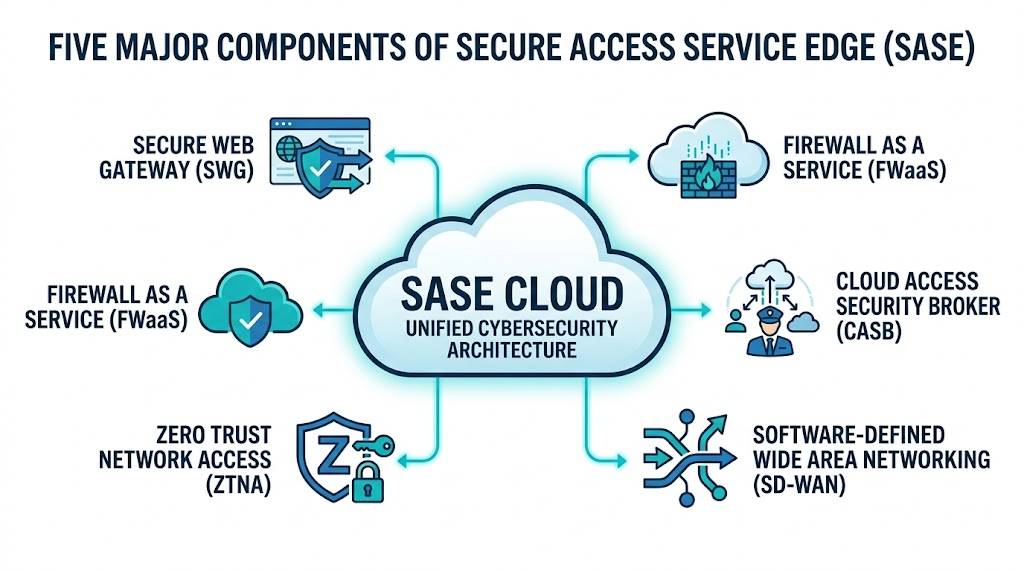
4. What Are the Components of SASE?
SASE combines five major technologies:
- Secure Web Gateway (SWG)
- Firewall as a Service (FWaaS)
- Cloud Access Security Broker (CASB)
- Zero Trust Network Access (ZTNA)
- Software-Defined Wide Area Networking (SD-WAN)
1. Secure Web Gateway (SWG)
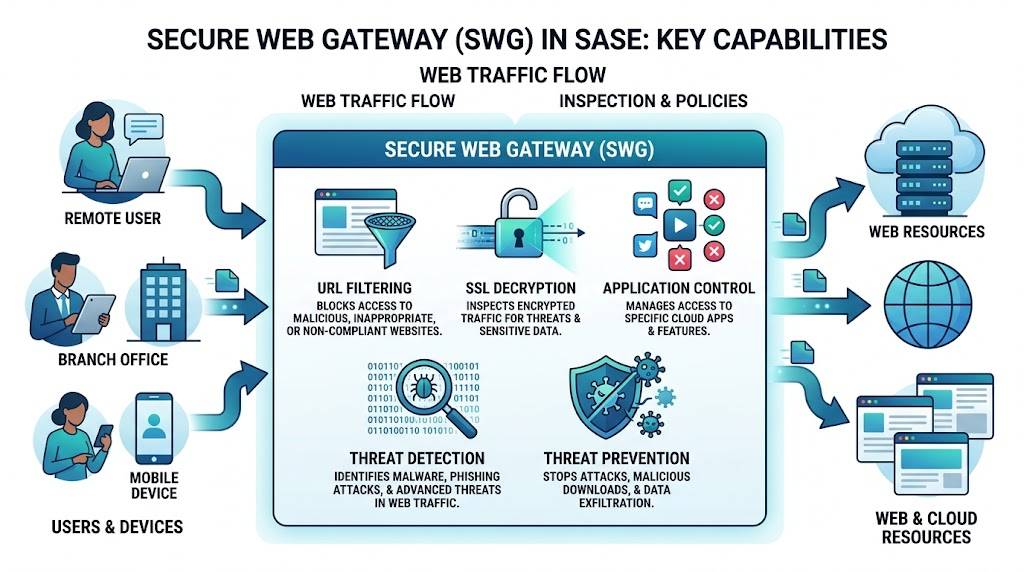
A Secure Web Gateway helps secure users when they access web resources. Its capabilities include:
- URL filtering
- SSL decryption
- Application control
- Threat detection
- Threat prevention
SWG therefore provides security controls for web traffic within the broader architecture.
2. Firewall as a Service (FWaaS)
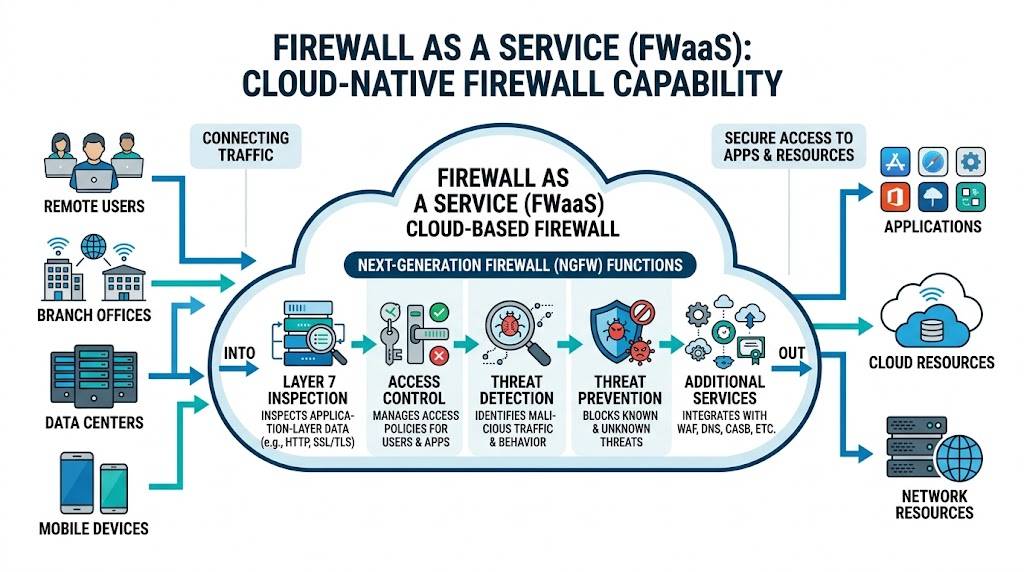
Firewall as a Service is a cloud-native firewall capability. It provides next-generation firewall functions through a cloud-based service.
FWaaS can provide:
- Layer 7 inspection
- Access control
- Threat detection
- Threat prevention
- Additional security services
3. Cloud Access Security Broker (CASB)
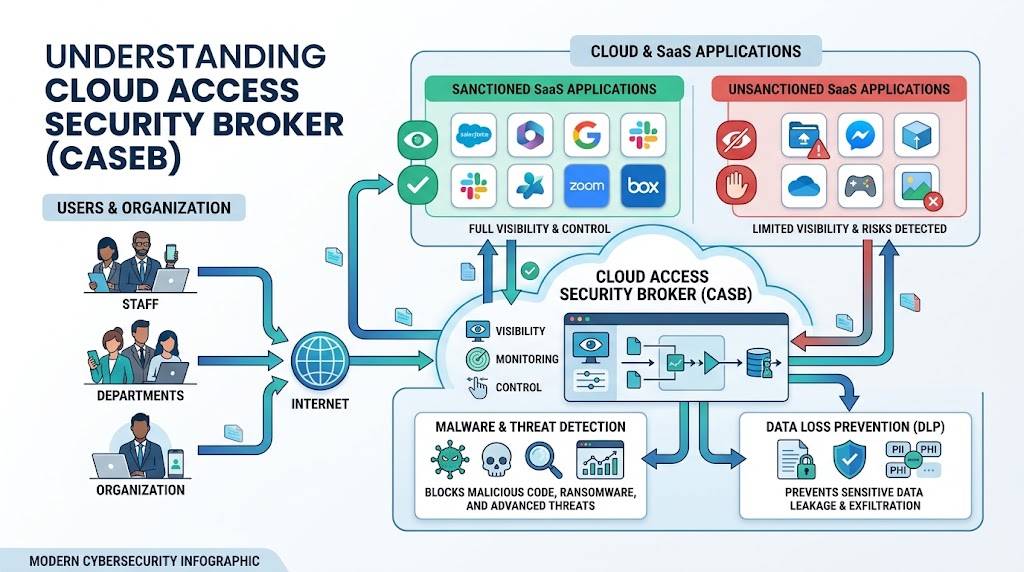
A Cloud Access Security Broker helps organizations monitor and control the use of cloud applications.
CASB can provide visibility into sanctioned and unsanctioned SaaS applications, detect malware and other threats, and provide visibility and control for data loss prevention.
4. Zero Trust Network Access (ZTNA)
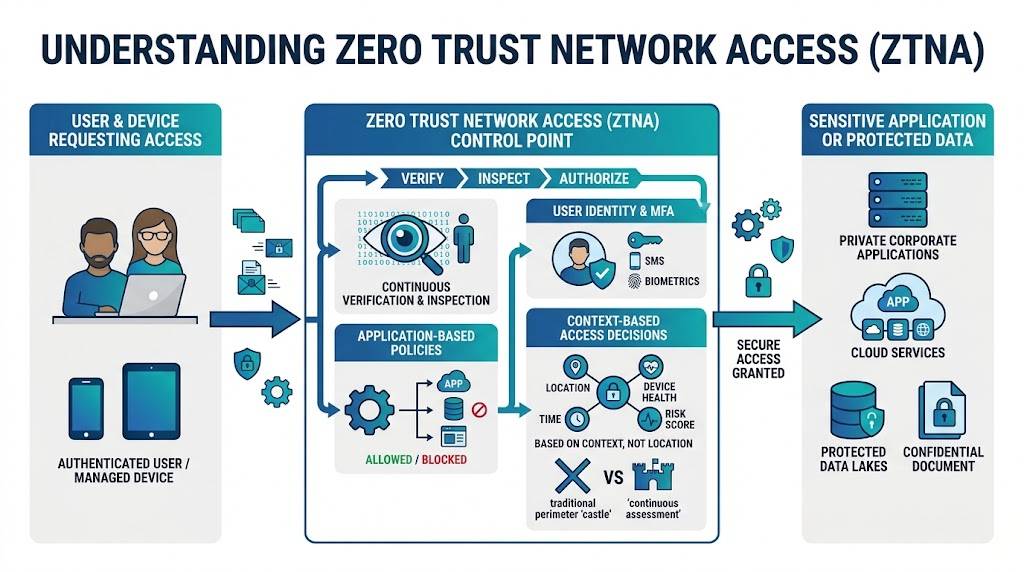
Zero Trust Network Access continuously verifies access and inspects connections.
ZTNA uses identity and application-based policies to control access to sensitive applications and data. This supports a security approach in which access decisions are based on context rather than simply trusting a user’s network location.
5. Software-Defined Wide Area Networking (SD-WAN)
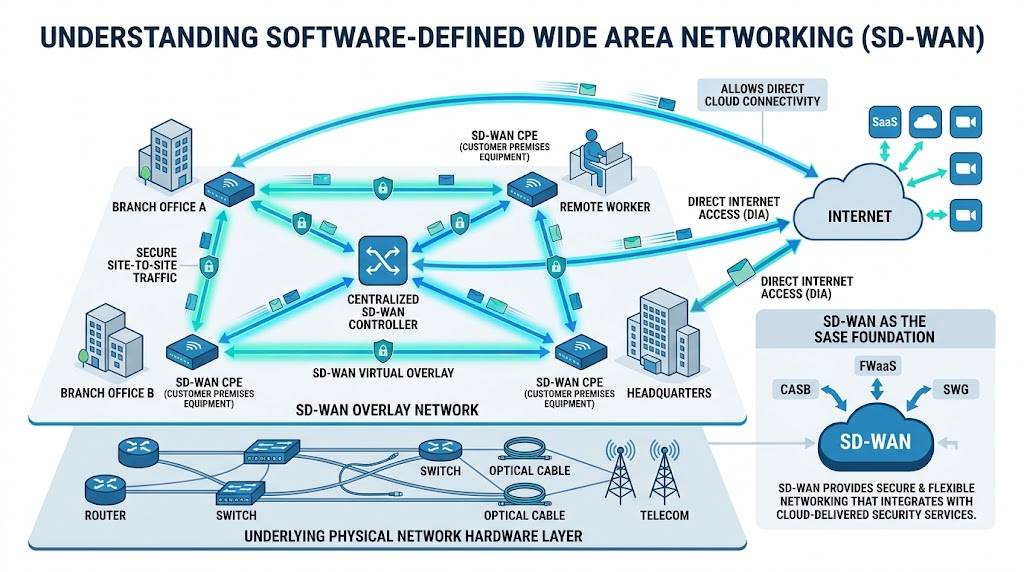
SD-WAN creates an overlay network that is separated from the underlying physical network hardware.
It provides flexibility for securely moving traffic between sites and for connecting directly to the internet.
Within SASE, SD-WAN provides the networking foundation that works together with cloud-delivered security services.
5. What Are the Use Cases for SASE?
SASE can support several modern networking and security use cases, including:
- Hybrid workforces
- Branch and retail environments
- Cloud and digital transformation
- Global connectivity
- Migration from MPLS to SD-WAN
Hybrid Workforce
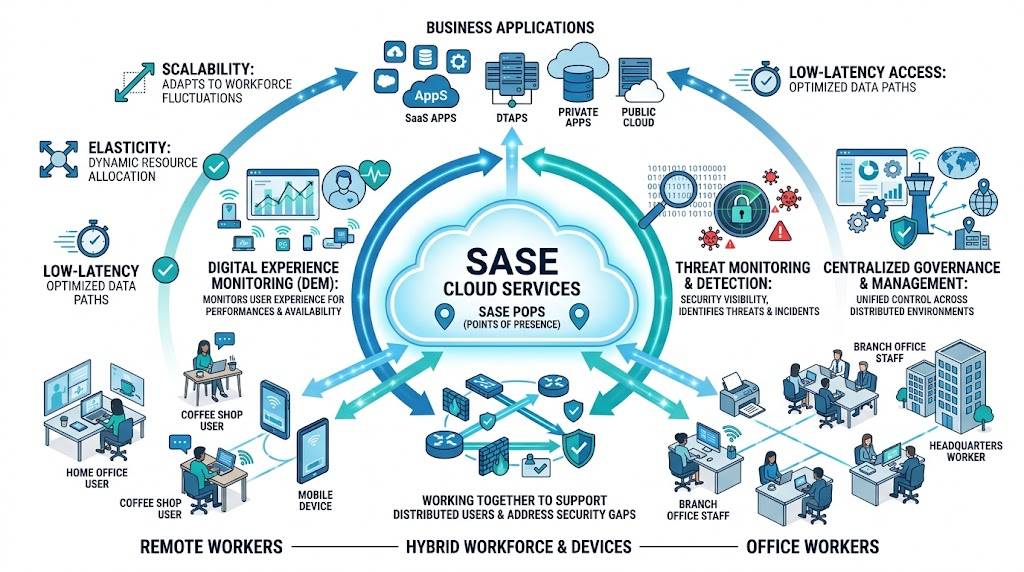
SASE can support hybrid workforces by providing scalability, elasticity, and low-latency access to applications.
Application-specific performance capabilities and Digital Experience Monitoring (DEM) can help organizations monitor the user experience.
By combining networking and security, SASE can also improve threat monitoring and detection while helping organizations address security gaps.
SASE can additionally provide centralized governance and management across distributed environments.
Branch and Retail
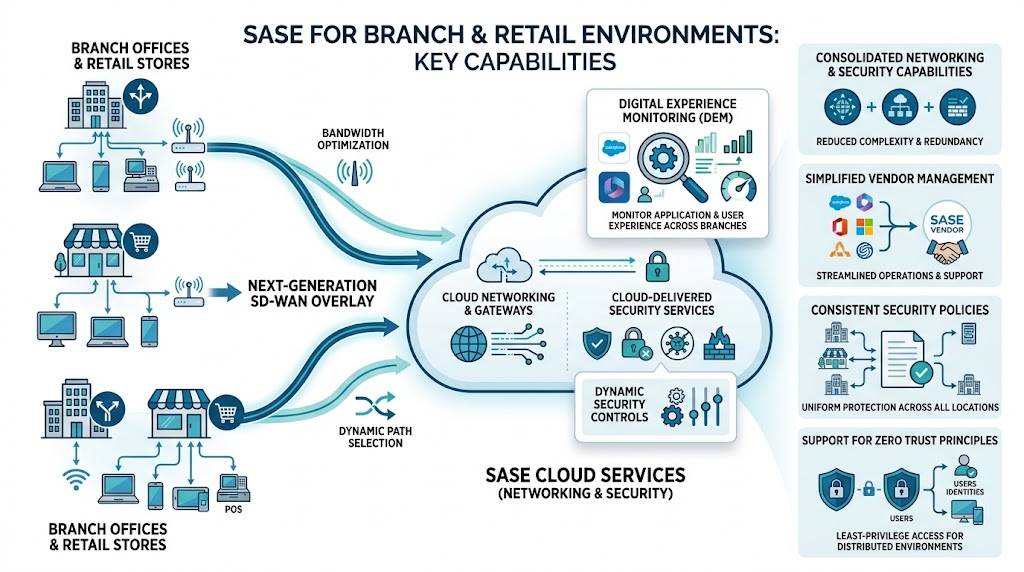
Branch and retail environments can use next-generation SD-WAN capabilities to optimize bandwidth and apply dynamic security controls.
Digital Experience Monitoring can help organizations monitor application and user experience.
SASE can also reduce expenses and simplify vendor management by consolidating networking and security capabilities.
Consistent policies and simplified management can strengthen data security while supporting Zero Trust principles.
Cloud and Digital Transformation
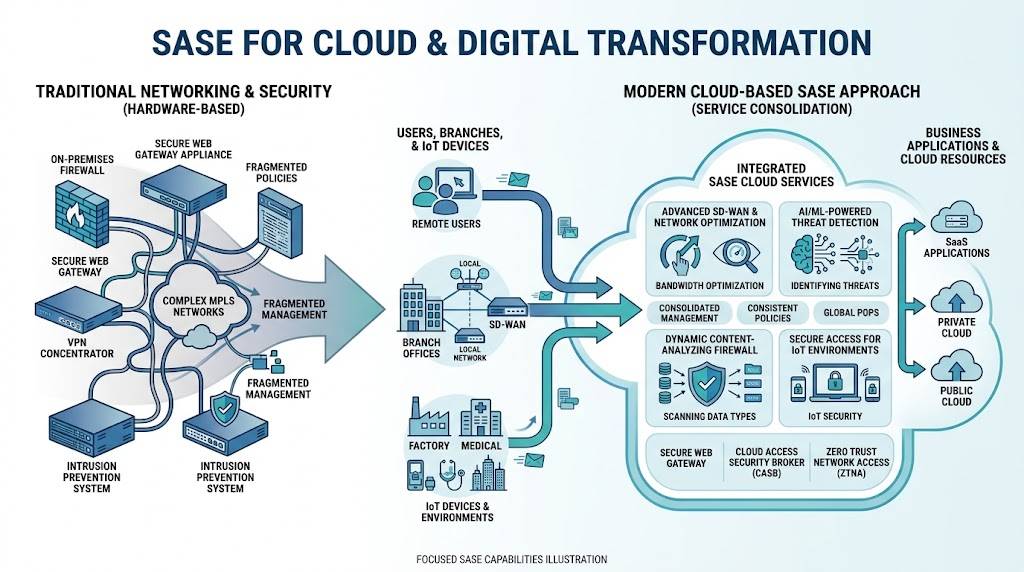
SASE can consolidate security services and reduce the limitations associated with traditional hardware-based security deployments.
Integrated services can support optimized branch connectivity, while advanced SD-WAN capabilities can provide additional bandwidth and network visibility.
AI and machine learning can support threat detection. Dynamic firewall capabilities can analyze content, while secure protocols can help support IoT environments.
Global Connectivity
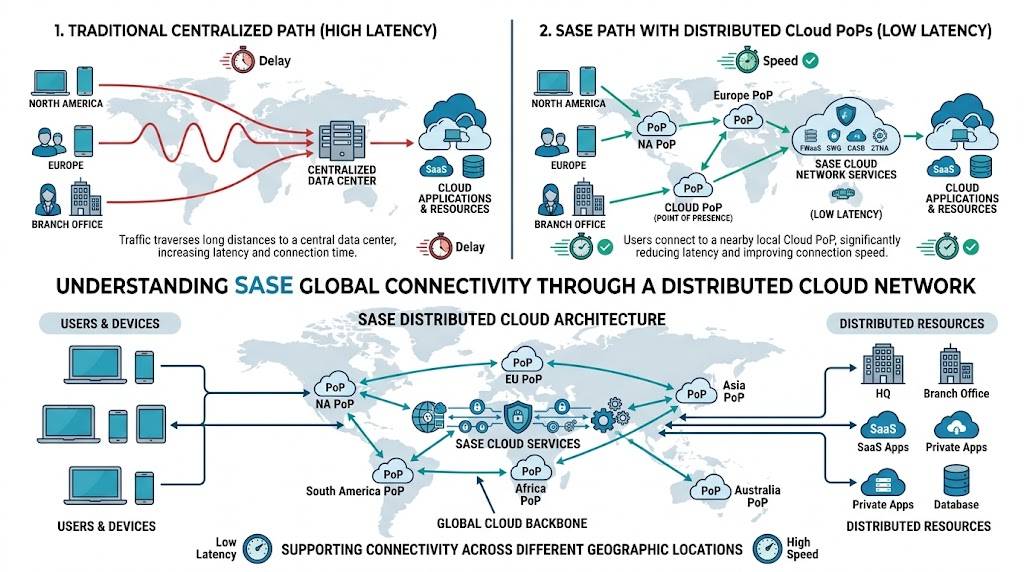
SASE can provide a distributed global network that allows users to connect through cloud Points of Presence (PoPs).
Instead of sending traffic through centralized data centers, SASE allows users to connect through a nearby PoP. This can help reduce latency and improve connection speed.
A distributed cloud architecture therefore supports connectivity across geographically dispersed users and resources.
Migrating From MPLS to SD-WAN
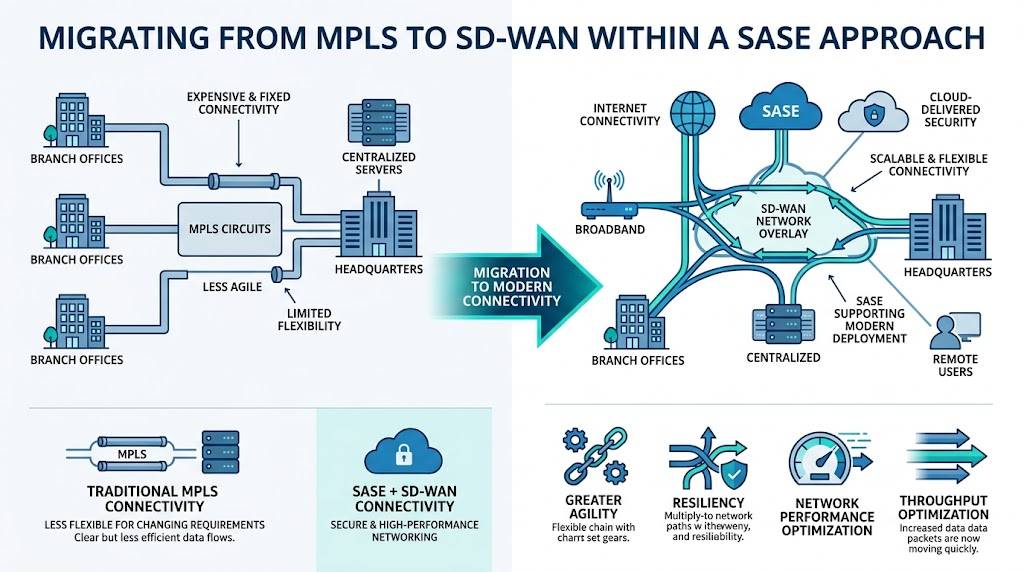
MPLS can be expensive and less flexible for organizations with changing connectivity requirements.
SASE provides a path toward scalable and cost-effective SD-WAN deployments. Internet connectivity can provide secure and high-performance networking, while broadband can offer lower-cost and more flexible connectivity options.
SD-WAN can provide greater agility and resiliency while optimizing network performance and throughput.
SASE and SD-WAN deployments can also be faster than traditional network deployments, with deployments typically taking days or hours depending on the environment.
6. What Are the Benefits of SASE?
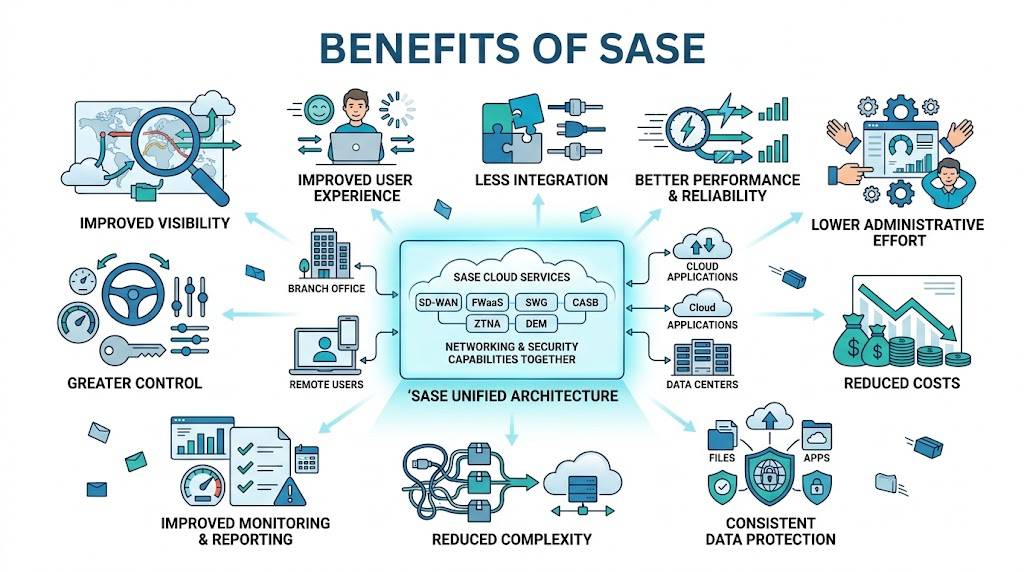
SASE can provide several benefits for organizations operating modern distributed networks.
Improved Visibility
SASE can provide visibility across hybrid environments, helping organizations understand users, applications, data, and network activity.
Greater Control
Layer 7 capabilities can provide greater control over users, data, and applications.
Improved Monitoring and Reporting
SASE can bring monitoring and reporting capabilities together within a unified architecture.
Reduced Complexity
Combining networking and security services can reduce architectural complexity and simplify management.
Consistent Data Protection
SASE can apply consistent security and data protection policies across distributed users and environments.
Reduced Costs
Consolidating networking and security capabilities can help reduce infrastructure and operational costs.
Lower Administrative Effort
A unified architecture can reduce administrative time and effort by reducing the need to manage multiple separate technologies.
Less Integration
Integrating networking and security services into a unified platform can reduce the amount of separate technology integration required.
Better Performance and Reliability
SD-WAN capabilities such as load balancing, traffic aggregation, and failover can improve network performance and reliability.
Improved User Experience
Digital Experience Monitoring can help organizations monitor user experience without requiring additional software or hardware.
7. What Are the Potential SASE Implementation Challenges?
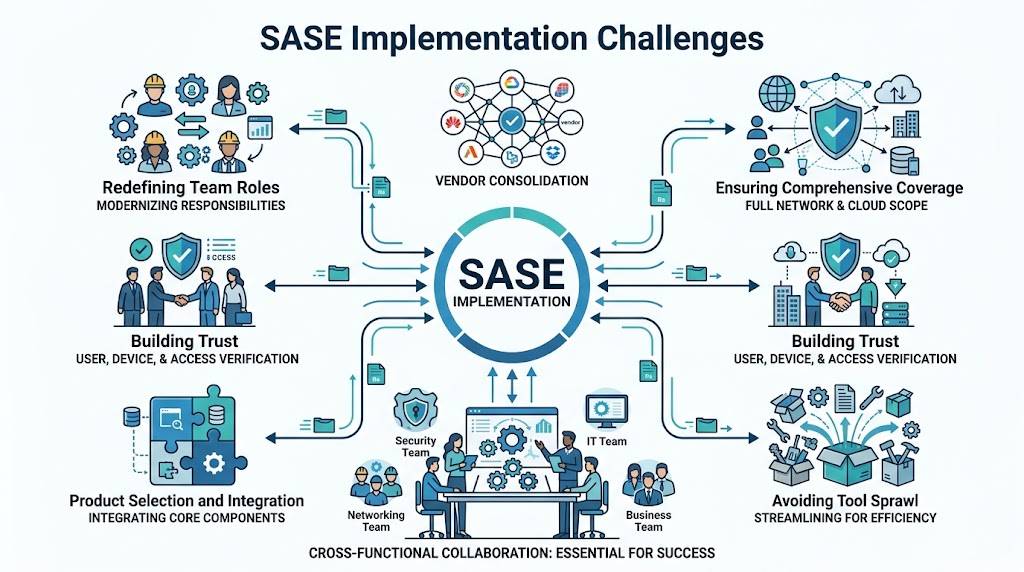
Although SASE can simplify networking and security, implementation can introduce several challenges.
Redefining Team Roles
Organizations may need to change how networking and security teams work together. Successful adoption requires collaboration across different teams.
Managing Vendor Complexity
Choosing and managing SASE technologies can become complex, particularly when multiple products and services are involved.
Ensuring Comprehensive Coverage
Organizations with many branches may require a combination of cloud-based and on-premises capabilities to achieve comprehensive coverage.
Building Trust
SASE adoption can require organizations to establish confidence in cloud-delivered networking and security services.
Product Selection and Integration
Organizations need to evaluate how SASE products integrate with existing technologies.
Avoiding Tool Sprawl
Adding more security products without proper consolidation can increase complexity instead of reducing it.
A collaborative approach between networking, security, IT, compliance, and business teams can help address these challenges.
8. How to Choose a SASE Provider
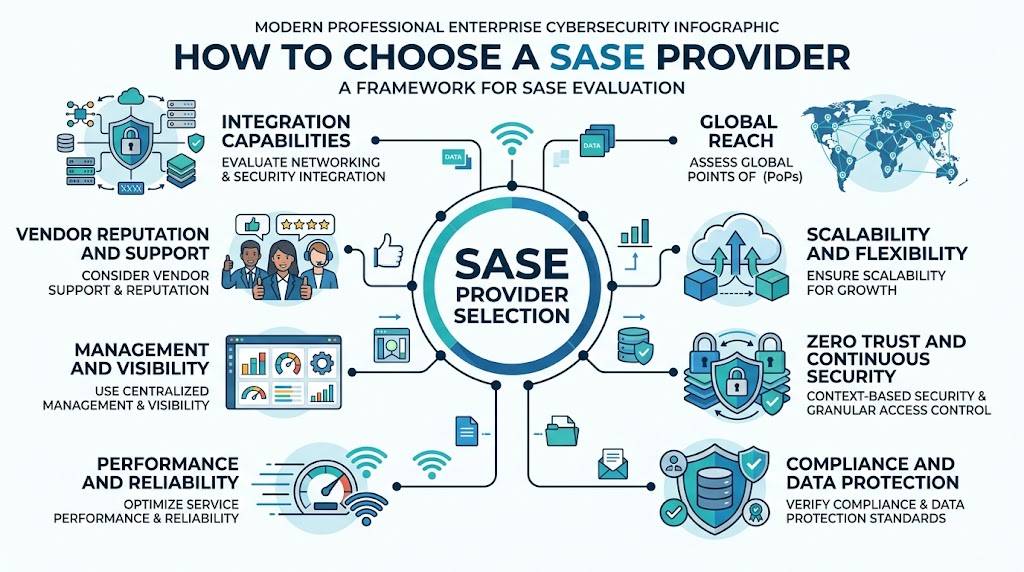
Organizations should evaluate several factors when selecting a SASE provider.
1. Integration Capabilities
Look for a platform that integrates networking and security capabilities effectively.
A more homogeneous platform can provide a more unified experience than combining unrelated technologies acquired or managed separately.
2. Global Reach
A SASE provider should have broad Points of Presence (PoPs) to support users and applications across different geographic locations.
3. Scalability and Flexibility
Evaluate the provider’s ability to support increasing traffic capacity and network expansion.
A flexible, cloud-native architecture can help organizations adapt as requirements change.
4. Zero Trust and Continuous Security
The platform should support context-based security policies, granular access control, and continuous assessment of security posture.
5. Compliance and Data Protection
Organizations should evaluate relevant compliance certifications and data protection capabilities.
Depending on the organization’s requirements, areas such as GDPR, HIPAA, and PCI-DSS may need to be considered.
6. Performance and Reliability
Review service-level agreements (SLAs) and available performance and reliability guarantees.
Financially backed SLAs can provide additional assurance around service commitments.
7. Management and Visibility
A centralized management dashboard can simplify administration and provide visibility across the SASE environment.
Organizations can request demonstrations to evaluate reporting, visibility, and management capabilities.
8. Vendor Reputation and Support
Review customer feedback, case studies, references, and available trials when evaluating providers.
9. How to Execute a Successful SASE Implementation in 6 Steps
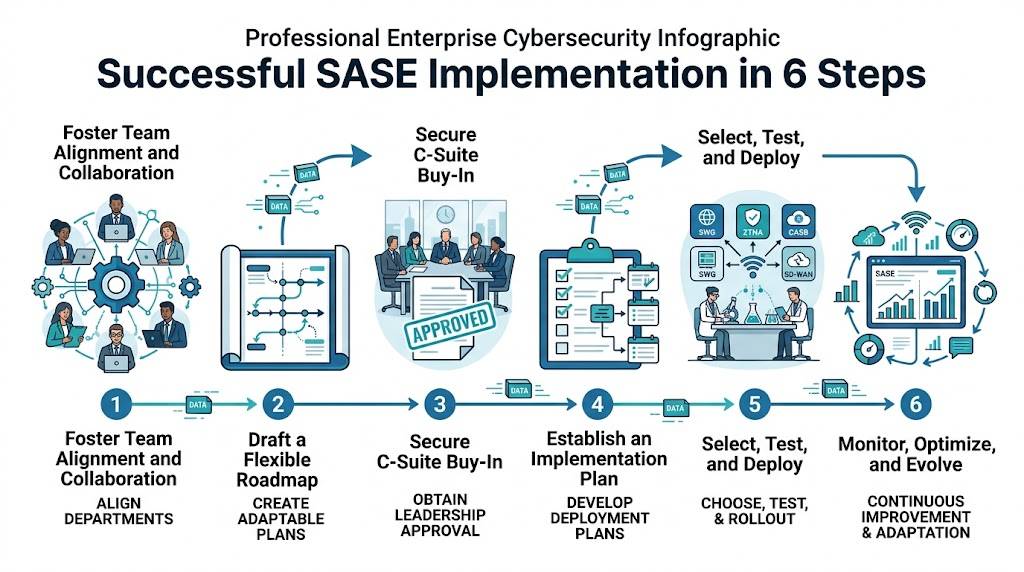
Step 1: Foster Team Alignment and Collaboration
SASE adoption requires cooperation between networking, security, IT, compliance, and business teams.
Organizations can use a DevOps-style evolution model in SASE to improve collaboration.
Leadership teams and vendors should also receive appropriate SASE education and training.
Tip: Create a cross-functional team and use workshops to align IT, security, compliance, and business requirements.
Step 2: Draft a Flexible Roadmap
Create a roadmap that supports progressive SASE adoption while remaining aligned with IT and business goals.
Organizations can work with vendors or managed service providers while gradually combining SD-WAN and security capabilities.
The SASE roadmap should support the convergence and progression of networking and security services.
Step 3: Secure C-Suite Buy-In
Explain the business value of SASE to senior leadership.
Key considerations include:
- Potential cost reduction
- Reduced number of vendors
- Improved security
- Business and operational benefits
Organizations should measure and report results.
Tip: Compare current SASE costs with projected costs and evaluate potential savings, downtime, and improvements in agility.
Step 4: Establish an Implementation Plan
Define the objectives of the SASE implementation.
Analyze the existing network and identify areas that need improvement.
Organizations should also evaluate existing skills and technology to understand what is already available and what may need to change.
Step 5: Select, Test, and Deploy
Select a SASE solution that is compatible with existing technologies.
Evaluate how the solution integrates with current tools.
Before broad SASE deployment, test the solution in a controlled environment.
Tip: Use pilot deployments or phased rollouts to support a controlled transition.
Step 6: Monitor, Optimize, and Evolve
After deployment, continue monitoring the environment.
Evaluate SASE performance and security requirements and make adjustments as necessary.
Ongoing support, monitoring, and optimization help the SASE environment evolve with changing requirements.
10. What Are the Most Common SASE Myths?
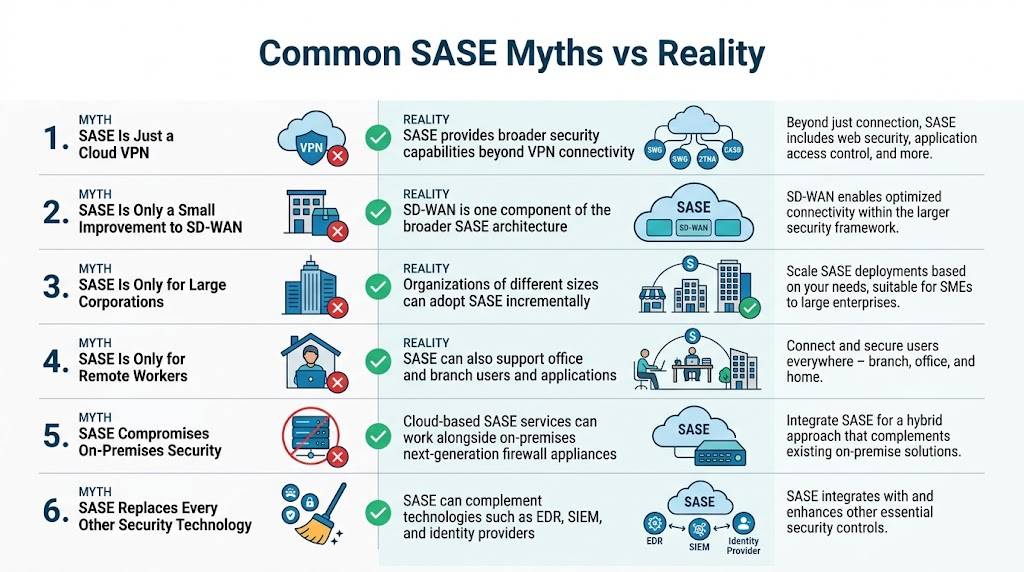
Several misconceptions can make SASE difficult to understand.
Myth 1: SASE Is Just a Cloud VPN
SASE is broader than a cloud-based VPN.
A VPN creates an encrypted tunnel for connectivity, but SASE provides broader security capabilities, including continuous inspection and context-aware policy enforcement.
Myth 2: SASE Is Only a Small Improvement to SD-WAN
SASE is not simply a minor extension of SD-WAN.
SD-WAN is one component of the broader SASE architecture, which also integrates multiple security capabilities.
Myth 3: SASE Is Only for Large Corporations
SASE can be used by organizations of different sizes.
Organizations can adopt capabilities incrementally, and some providers offer bundled or managed services.
Myth 4: SASE Is Only for Remote Workers
SASE is not limited to remote users.
It can also support users and applications located within office and branch environments.
Myth 5: SASE Compromises On-Premises Security
SASE does not necessarily require organizations to abandon on-premises security capabilities.
Cloud-based SASE services can work alongside on-premises next-generation firewall appliances.
Myth 6: SASE Replaces Every Other Security Technology
SASE is not intended to eliminate every existing security technology.
It can complement technologies such as Endpoint Detection and Response (EDR) and cloud workload protection.
APIs and connectors can also support SASE integration with technologies such as EDR, SIEM, and identity providers.
11. How Does SASE Work With Complementary Technologies?
SASE can work alongside technologies such as 5G, IoT, and Data Loss Prevention (DLP).
1. SASE and 5G
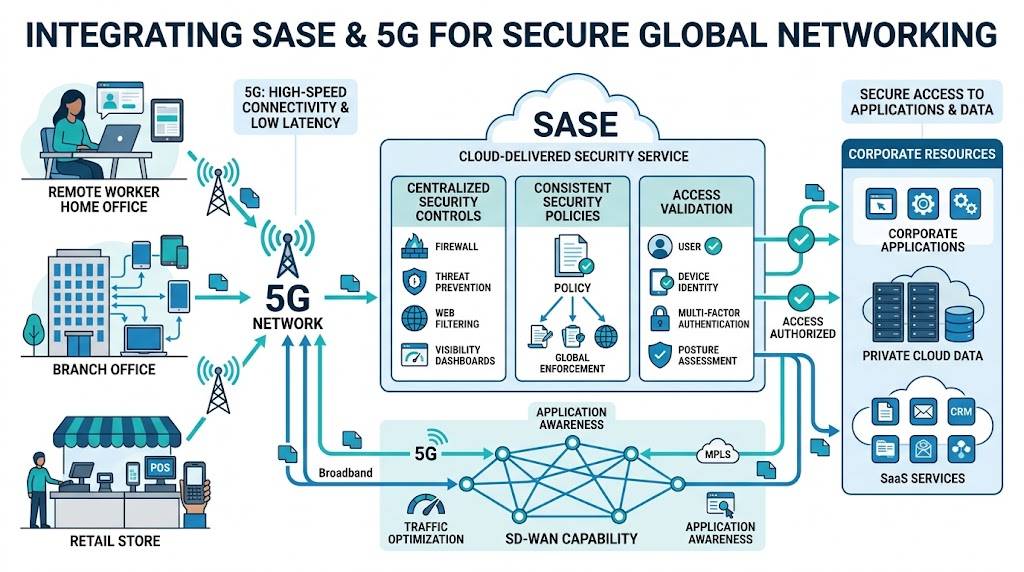
5G provides high-speed connectivity and low latency.
SASE can provide centralized security controls for 5G-connected users and devices. Routing 5G traffic through this architecture can help maintain consistent security policies across different locations.
Users can access corporate resources from diverse locations while security controls continue to validate access.
SD-WAN can further support this connectivity by managing traffic across available network paths.
2. SASE and IoT
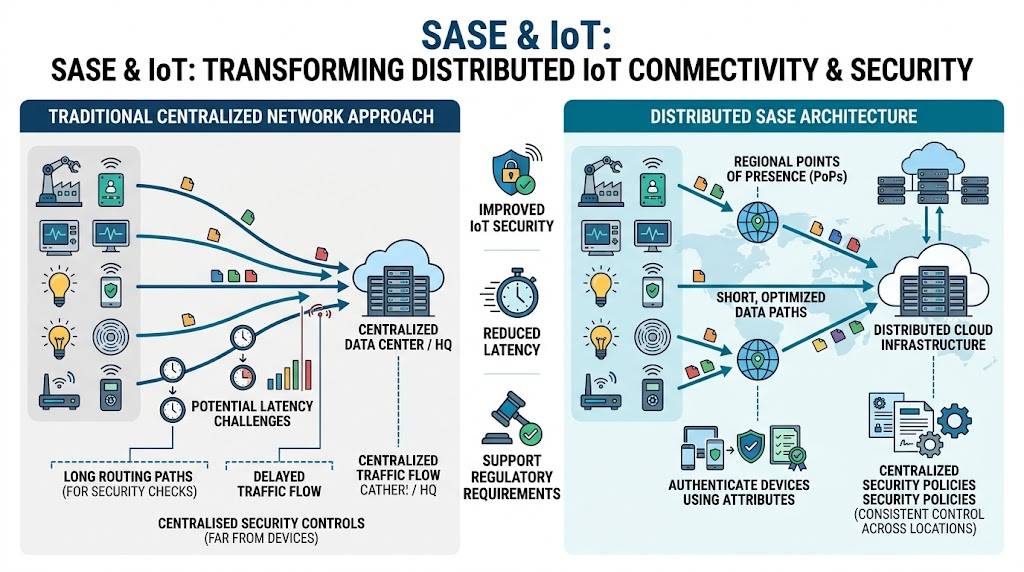
Traditional centralized networks can create routing and latency challenges for distributed IoT environments.
SASE can use distributed cloud infrastructure and multiple regional Points of Presence to bring security controls closer to connected devices.
Distributed PoPs can authenticate devices using device attributes while centralized policies provide consistent security controls.
This approach can help improve IoT security and reduce latency while supporting regulatory requirements.
3. SASE and Data Loss Prevention (DLP)
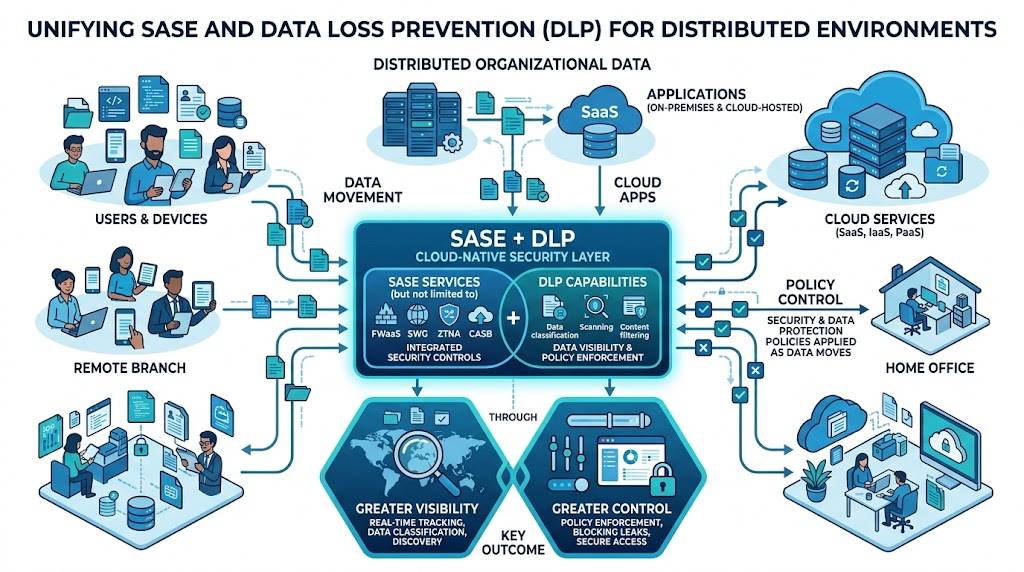
Data is increasingly distributed across users, applications, cloud services, and other environments.
Traditional DLP approaches may not provide sufficient visibility across these distributed environments.
SASE can combine DLP capabilities with cloud-native security services so that policies can be applied as data moves across the environment.
This provides greater visibility and control over organizational data.
12. Comparing SASE With Other Security and Technology Solutions
The following comparison summarizes how SASE relates to other networking and security approaches.
| Aspect | SD-WAN | SASE | CASB | ZTNA | SSE | Traditional Network Security | Firewall | Zero Trust | VPN |
|---|---|---|---|---|---|---|---|---|---|
Integration of networking/security | Networking-focused | Networking + security | Security-focused | Security architecture | Access-focused | Security services | Traditionally separated | Security-focused | Security model |
| Deployment focus | WAN connectivity | Cloud-delivered networking and security | Cloud application security | Security architecture | Application access | Cloud security | Perimeter/network | Network security | Identity and context |
| Primary benefit | Flexible WAN connectivity | Unified networking and security | SaaS visibility and control | Secure access architecture | Controlled application access | Consolidated security services | Network protection | Traffic control | Continuous verification |
| Suitability for modern work environments | High | High | High | High | High | High | More limited for distributed environments | High | High |
13. What Is the History of SASE?
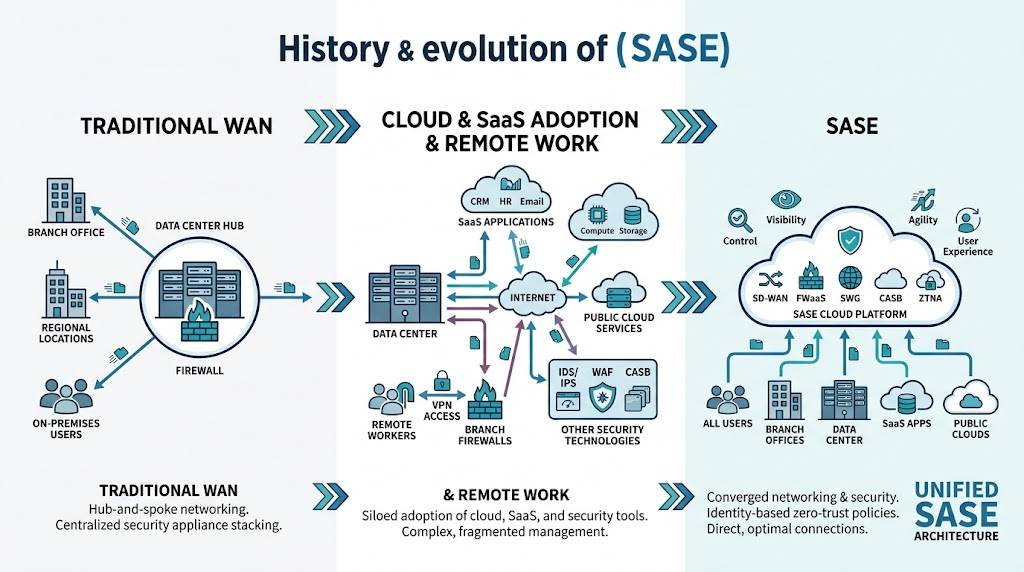
Traditional wide area networks often used a hub-and-spoke architecture in which traffic was routed through centralized locations.
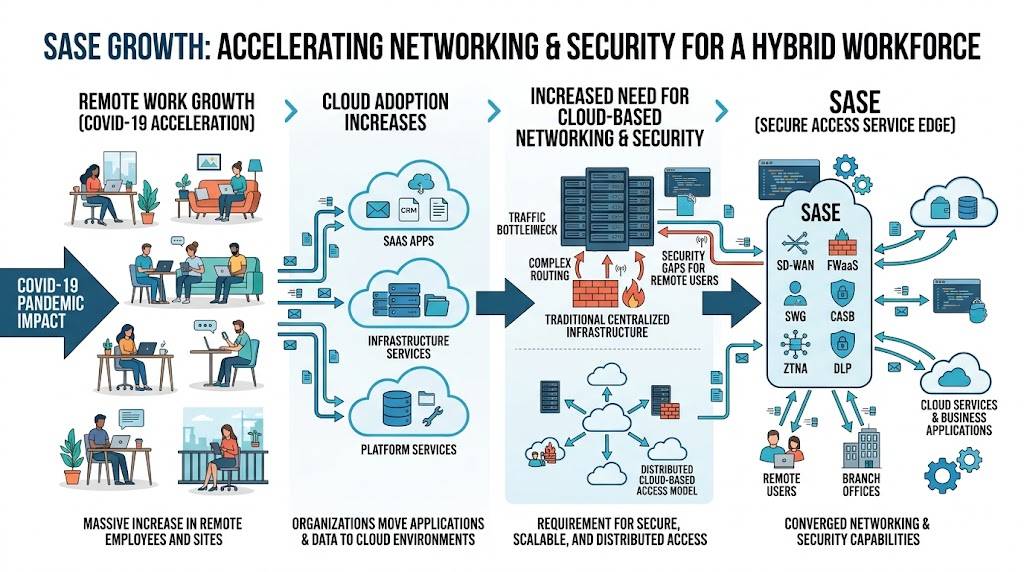
As organizations adopted cloud services and SaaS applications, traffic patterns changed. VPN usage increased alongside cloud adoption, while organizations also deployed branch firewalls and other security technologies.
Cloud services reduced dependence on traditional on-premises infrastructure and increased the need for new approaches to networking and security.
SASE emerged as an architecture designed to bring networking and security capabilities together.
The growth of services such as Office 365 and Azure also increased the need for effective traffic management and inspection.
The COVID-19 pandemic further accelerated remote work and contributed to increased interest in cloud-based networking and security architectures.
SASE FAQs
What does SASE stand for?
SASE stands for Secure Access Service Edge. It is a cloud-native architecture that combines networking and security capabilities.
What is the difference between SD-WAN and SASE?
SD-WAN focuses primarily on software-defined WAN connectivity. SASE is broader and combines SD-WAN with multiple cloud-delivered security capabilities.
What are the five main components of SASE?
The five main components are:
- Secure Web Gateway (SWG)
- Firewall as a Service (FWaaS)
- Cloud Access Security Broker (CASB)
- Zero Trust Network Access (ZTNA)
- Software-Defined Wide Area Networking (SD-WAN)
Is SASE better than a VPN?
SASE provides broader capabilities than a VPN. A VPN primarily provides encrypted connectivity, while SASE combines connectivity with security capabilities and continuous, context-aware inspection.
Does SASE replace VPN technology?
SASE provides capabilities beyond traditional VPN connectivity. Whether an organization replaces or continues using VPN technology depends on its existing architecture and requirements.
Is SASE the same as a firewall?
No. A firewall is one security capability, while SASE combines networking and multiple security technologies into a broader architecture.
Does SASE include SD-WAN?
Yes. SD-WAN is one of the five major technologies included within the SASE architecture.
What is the main promise of SASE?
The main goal of SASE is to bring networking and security capabilities together through a cloud-native architecture for modern distributed environments.
Is SASE a proxy?
SASE is not simply a proxy. It is a broader architecture that combines multiple networking and security capabilities.